Fortgeschrittener RayHunter 2026: Techniken und Fehlerbehebung

Table of Contents
Beherrsche fortgeschrittene RayHunter-Konfiguration, Fehlerbehebung und Optimierung zur Erkennung von IMSI-Catchern auf Expertenniveau
Kurzfassung
Der fortgeschrittene Einsatz von RayHunter erfordert durchdachte Konfigurationsstrategien, die Anpassung eigener Heuristiken und fundierte Kenntnisse zur Fehlerbehebung. Dieser Expertenleitfaden behandelt unter anderem die Optimierung von Heuristiken für bestimmte Bedrohungsumgebungen (bis zu 80 % weniger Fehlalarme), automatisierte Analyseabläufe über APIs, koordinierte Erkennung mit mehreren Geräten, die Integration fortgeschrittener Forensik und komplexe Fehlersuche. Zu den erweiterten Funktionen zählen Änderungen an config.toml für spezialisierte Umgebungen, Automatisierung über die REST API zur Integration in Unternehmen, fortgeschrittene QMDL/PCAP-Analyse, koordinierte Einsätze mehrerer Sensoren und ausgefeilte Algorithmen zur Korrelation von Bedrohungen. Mit einer geeigneten erweiterten Konfiguration erreichen erfahrene Nutzer eine Erkennungsgenauigkeit von über 99 % und eine Fehlalarmquote unter 1 %, während sie RayHunter in umfassende Security Operations Center und automatisierte Systeme zur Reaktion auf Bedrohungen integrieren.
Einführung in den fortgeschrittenen RayHunter-Betrieb
Der fortgeschrittene Einsatz von RayHunter geht weit über Installation und Grundkonfiguration hinaus. Für die Nutzung auf Expertenniveau brauchst du fundierte Kenntnisse in Mobilfunkprotokollen, HF-Analyse, Bedrohungsmodellierung und fortgeschrittener Systemintegration. Dieser Leitfaden behandelt die anspruchsvollen Techniken, die für professionelle Sicherheitsabläufe, Forschungsumgebungen und Situationen mit hohem Risiko bei der Überwachungserkennung erforderlich sind.
Der fortgeschrittene Einsatz von RayHunter umfasst:
- Eigene Heuristiken entwickeln und für bestimmte Bedrohungsumgebungen optimieren
- Automatisierung über APIs und Integration in Security Operations Center
- Mehrere Geräte koordinieren, um ein Gebiet umfassend abzudecken
- Fortgeschrittene Forensik integrieren und Mobilfunkanalysewerkzeuge einbinden
- Eigene Bedrohungsmodelle und umgebungsspezifische Konfigurationen
- Fehlerbehebung und Wartung auf Unternehmensniveau
Dieser Leitfaden setzt Grundkenntnisse zur Installation und Konfiguration von RayHunter voraus. Für fortgeschrittene Techniken brauchst du Kenntnisse zu Mobilfunkprotokollen (2G/3G/4G/LTE), HF-Analyse, Netzwerksicherheit und der Integration in ein Security Operations Center.

Fortgeschrittene Konfigurationsstrategien
Eigene Heuristiken optimieren
Die Erkennungsleistung von RayHunter hängt stark davon ab, ob die Heuristiken passend für die jeweilige Einsatzumgebung konfiguriert sind. Erfahrene Nutzer können die Erkennungsgenauigkeit deutlich steigern und zugleich Fehlalarme reduzieren, indem sie die Heuristiken sorgfältig abstimmen.
Heuristikprofile für bestimmte Umgebungen
Konfiguration für dicht besiedelte Städte:
[heuristics]
# Reduce sensitivity for busy urban environments
connection_release_detection = { enabled = true, sensitivity = "low", timeout = 30 }
imsi_request_detection = { enabled = true, threshold = 3, window = 60 }
null_cipher_detection = { enabled = true, immediate_alert = false }
sib_downgrade_detection = { enabled = true, sensitivity = "medium" }
incomplete_sib_detection = { enabled = false }  # High false positive rate in urban areas

[filtering]
# Advanced filtering for urban environments
tower_density_threshold = 20
legitimate_carrier_whitelist = ["Verizon", "AT&T", "T-Mobile"]
frequency_hopping_tolerance = 5
Konfiguration für dünn besiedelte ländliche Gebiete:
[heuristics]
# Increase sensitivity for sparse environments
connection_release_detection = { enabled = true, sensitivity = "high", timeout = 10 }
imsi_request_detection = { enabled = true, threshold = 1, window = 30 }
null_cipher_detection = { enabled = true, immediate_alert = true }
sib_downgrade_detection = { enabled = true, sensitivity = "high" }
incomplete_sib_detection = { enabled = true, threshold = 2 }

[filtering]
# Minimal filtering for rural environments
tower_density_threshold = 5
legitimate_carrier_whitelist = []
frequency_hopping_tolerance = 1
Konfiguration für Veranstaltungen mit hohen Sicherheitsanforderungen:
[heuristics]
# Maximum sensitivity for high-risk scenarios
connection_release_detection = { enabled = true, sensitivity = "maximum", timeout = 5 }
imsi_request_detection = { enabled = true, threshold = 1, window = 15 }
null_cipher_detection = { enabled = true, immediate_alert = true, block_connection = true }
sib_downgrade_detection = { enabled = true, sensitivity = "maximum" }
incomplete_sib_detection = { enabled = true, threshold = 1 }
test_heuristic = { enabled = false }  # Never enable test mode during operations

[alerting]
# Immediate alerts for high-security scenarios
alert_threshold = "low"
immediate_notification = true
multi_channel_alerts = true
Eigene Heuristiken entwickeln
Erfahrene Nutzer können eigene Erkennungsheuristiken entwickeln, indem sie die Konfiguration und Analyselogik von RayHunter anpassen:
Eigene Heuristik zur Zeitanalyse:
[custom_heuristics]
# Custom timing-based detection
timing_anomaly_detection = {
    enabled = true,
    baseline_establishment = 300,  # 5 minutes baseline
    deviation_threshold = 3.0,     # 3 standard deviations
    minimum_samples = 50,
    alert_on_first_deviation = false
}

# Advanced pattern recognition
cell_tower_behavior_analysis = {
    enabled = true,
    learning_period = 3600,        # 1 hour learning
    pattern_memory = 168,          # 7 days pattern retention
    anomaly_sensitivity = 0.85,    # 85% confidence threshold
    behavioral_baseline = "adaptive"
}
Heuristik zur geografischen Korrelation:
[geo_correlation]
# Location-based threat assessment
enabled = true
gps_accuracy_threshold = 10        # 10 meter accuracy required
movement_speed_threshold = 50      # 50 km/h maximum reasonable speed
stationary_threshold = 100         # 100 meter stationary radius
suspicious_location_database = "/data/rayhunter/suspicious_locations.db"

# Coordinated detection across multiple devices
multi_device_correlation = {
    enabled = true,
    correlation_radius = 1000,     # 1km correlation radius
    time_synchronization = 5,      # 5 second time sync tolerance
    consensus_threshold = 0.67     # 67% of devices must agree
}
Fortgeschrittenes Energiemanagement
Lange Einsätze erfordern Energiestrategien, die über eine einfache Akkuoptimierung hinausgehen:
Adaptives Energiemanagement:
[power_management]
# Dynamic power scaling based on threat level
adaptive_scaling = true
baseline_power_mode = "balanced"
high_alert_power_mode = "maximum_performance"
low_activity_power_mode = "extended_battery"

# Scheduled operation modes
scheduled_modes = [
    { time = "00:00-06:00", mode = "low_power", days = ["monday", "tuesday", "wednesday", "thursday", "friday"] },
    { time = "06:00-22:00", mode = "high_sensitivity", days = ["saturday", "sunday"] },
    { time = "22:00-24:00", mode = "balanced", days = "all" }
]

# Battery-level triggered mode changes
battery_thresholds = {
    "90%" = "maximum_performance",
    "50%" = "balanced",
    "25%" = "extended_battery",
    "10%" = "emergency_detection_only"
}
Koordiniertes Energiemanagement für mehrere Geräte:
[coordinated_power]
# Coordinate power management across multiple devices
device_roles = ["primary", "secondary", "backup"]
role_switching_enabled = true
battery_level_sharing = true
automatic_failover = true

# Advanced sleep/wake coordination
coordinated_sleep_cycles = {
    enabled = true,
    sleep_rotation_interval = 300,  # 5 minutes
    minimum_active_devices = 2,
    overlap_period = 30             # 30 seconds overlap
}
Fortgeschrittene Analysetechniken
Eigene PCAP- und QMDL-Analyse
RayHunter erstellt detaillierte Mitschnitte von Mobilfunkprotokollen. Fortgeschrittene Analysetechniken holen daraus möglichst viele verwertbare Informationen.
rayhunter-check fortgeschritten nutzen
Abläufe für Stapelanalysen:
#!/bin/bash
# Advanced batch analysis script for multiple recordings

ANALYSIS_DIR="/data/rayhunter/analysis"
RECORDINGS_DIR="/data/rayhunter/recordings"
OUTPUT_DIR="/data/rayhunter/reports"

# Process all recordings with custom parameters
for recording in "$RECORDINGS_DIR"/*.qmdl; do
    filename=$(basename "$recording" .qmdl)
    echo "Processing $filename..."

    # Standard analysis
    rayhunter-check -p "$recording" --json > "$OUTPUT_DIR/${filename}_standard.json"

    # Debug analysis with extended output
    rayhunter-check -d -p "$recording" --verbose > "$OUTPUT_DIR/${filename}_debug.log"

    # Custom heuristic analysis
    rayhunter-check -p "$recording" --config "/etc/rayhunter/custom_analysis.toml" \
        --output-format json > "$OUTPUT_DIR/${filename}_custom.json"

    # Threat correlation analysis
    rayhunter-check -p "$recording" --correlate-threats \
        --baseline "$ANALYSIS_DIR/baseline.qmdl" > "$OUTPUT_DIR/${filename}_correlation.json"
done

# Generate consolidated report
python3 /opt/rayhunter/analysis/consolidate_reports.py "$OUTPUT_DIR" > "$OUTPUT_DIR/consolidated_analysis.html"
Fortgeschrittene Filterung und Analyse:
# Custom analysis with specific focus areas
rayhunter-check -p recording.qmdl \
    --focus-heuristics "imsi_request,null_cipher" \
    --time-range "14:30-15:45" \
    --frequency-bands "1900,850" \
    --operator-filter "unknown" \
    --confidence-threshold 0.8

# Comparative analysis between recordings
rayhunter-check --compare recording1.qmdl recording2.qmdl \
    --baseline-period 300 \
    --anomaly-detection \
    --statistical-analysis

# Integration with external tools
rayhunter-check -p recording.qmdl --export-wireshark | \
    tshark -r - -Y "gsm || lte" -T json > cellular_traffic.json
Eigene Analyseskripte
Python-Integration für fortgeschrittene Analysen:
#!/usr/bin/env python3
"""
Advanced RayHunter Analysis Integration
Provides sophisticated analysis capabilities for RayHunter data
"""

import json
import sqlite3
import pandas as pd
from datetime import datetime, timedelta
import numpy as np
from scipy import stats
import matplotlib.pyplot as plt

class RayHunterAnalyzer:
    def __init__(self, database_path="/data/rayhunter/analysis.db"):
        self.db_path = database_path
        self.init_database()

    def init_database(self):
        """Initialize analysis database with custom schema"""
        conn = sqlite3.connect(self.db_path)
        cursor = conn.cursor()

        # Create advanced analysis tables
        cursor.execute('''
            CREATE TABLE IF NOT EXISTS threat_events (
                id INTEGER PRIMARY KEY,
                timestamp TEXT,
                device_id TEXT,
                threat_type TEXT,
                confidence_score REAL,
                location_lat REAL,
                location_lon REAL,
                cellular_parameters TEXT,
                correlated_events TEXT
            )
        ''')

        cursor.execute('''
            CREATE TABLE IF NOT EXISTS baseline_data (
                id INTEGER PRIMARY KEY,
                location_hash TEXT,
                time_of_day INTEGER,
                day_of_week INTEGER,
                cellular_environment TEXT,
                normal_patterns TEXT,
                anomaly_thresholds TEXT
            )
        ''')

        conn.commit()
        conn.close()

    def process_rayhunter_json(self, json_file_path):
        """Process RayHunter JSON output for advanced analysis"""
        with open(json_file_path, 'r') as f:
            data = json.load(f)

        # Extract and normalize threat events
        events = []
        for alert in data.get('alerts', []):
            event = {
                'timestamp': alert.get('timestamp'),
                'threat_type': alert.get('heuristic'),
                'confidence_score': self.calculate_confidence_score(alert),
                'cellular_parameters': json.dumps(alert.get('cellular_data', {})),
                'device_location': alert.get('location', {})
            }
            events.append(event)

        return events

    def calculate_confidence_score(self, alert):
        """Calculate advanced confidence score based on multiple factors"""
        base_confidence = alert.get('confidence', 0.5)

        # Factor in multiple data points
        factors = {
            'signal_strength': alert.get('signal_strength', 0) / 100,
            'timing_consistency': alert.get('timing_score', 0.5),
            'protocol_compliance': alert.get('protocol_score', 0.5),
            'environmental_context': alert.get('environment_score', 0.5)
        }

        # Weighted confidence calculation
        weights = {'signal_strength': 0.3, 'timing_consistency': 0.25,
                  'protocol_compliance': 0.25, 'environmental_context': 0.2}

        weighted_confidence = sum(factors[k] * weights[k] for k in factors)
        return min(base_confidence + weighted_confidence, 1.0)

    def correlation_analysis(self, events, time_window=300):
        """Perform temporal and spatial correlation analysis"""
        correlations = []

        for i, event1 in enumerate(events):
            for j, event2 in enumerate(events[i+1:], i+1):
                time_diff = abs((datetime.fromisoformat(event1['timestamp']) -
                               datetime.fromisoformat(event2['timestamp'])).total_seconds())

                if time_diff <= time_window:
                    correlation = {
                        'event1_id': i,
                        'event2_id': j,
                        'time_difference': time_diff,
                        'correlation_strength': self.calculate_correlation_strength(event1, event2),
                        'threat_escalation': self.assess_threat_escalation(event1, event2)
                    }
                    correlations.append(correlation)

        return correlations

    def calculate_correlation_strength(self, event1, event2):
        """Calculate correlation strength between two events"""
        # Implement sophisticated correlation algorithm
        similarity_factors = []

        # Threat type similarity
        if event1['threat_type'] == event2['threat_type']:
            similarity_factors.append(0.4)
        elif self.are_related_threats(event1['threat_type'], event2['threat_type']):
            similarity_factors.append(0.2)

        # Confidence score similarity
        confidence_diff = abs(event1['confidence_score'] - event2['confidence_score'])
        similarity_factors.append(1.0 - confidence_diff)

        return np.mean(similarity_factors)

    def generate_threat_report(self, analysis_period_hours=24):
        """Generate comprehensive threat assessment report"""
        end_time = datetime.now()
        start_time = end_time - timedelta(hours=analysis_period_hours)

        # Query database for recent events
        conn = sqlite3.connect(self.db_path)
        query = '''
            SELECT * FROM threat_events
            WHERE timestamp BETWEEN ? AND ?
            ORDER BY timestamp DESC
        '''

        df = pd.read_sql_query(query, conn, params=(start_time.isoformat(), end_time.isoformat()))
        conn.close()

        if df.empty:
            return {"status": "no_threats", "period": analysis_period_hours}

        # Generate statistical analysis
        threat_stats = {
            'total_events': len(df),
            'unique_threat_types': df['threat_type'].nunique(),
            'average_confidence': df['confidence_score'].mean(),
            'threat_distribution': df['threat_type'].value_counts().to_dict(),
            'temporal_patterns': self.analyze_temporal_patterns(df),
            'risk_assessment': self.calculate_risk_level(df)
        }

        return threat_stats
Automatisierung über APIs
Die REST API von RayHunter ermöglicht fortgeschrittene Automatisierung und die Integration in Sicherheitssysteme von Unternehmen.
Automatisierte Überwachungsskripte
Kontinuierliche Überwachung automatisieren:
#!/usr/bin/env python3
"""
Enterprise RayHunter Monitoring System
Automated threat detection and response integration
"""

import requests
import time
import json
import logging
from datetime import datetime
import subprocess
import smtplib
from email.mime.text import MIMEText

class RayHunterMonitor:
    def __init__(self, device_configs):
        self.devices = device_configs
        self.alert_handlers = []
        self.setup_logging()

    def setup_logging(self):
        """Configure enterprise-grade logging"""
        logging.basicConfig(
            level=logging.INFO,
            format='%(asctime)s - %(name)s - %(levelname)s - %(message)s',
            handlers=[
                logging.FileHandler('/var/log/rayhunter/monitor.log'),
                logging.StreamHandler()
            ]
        )
        self.logger = logging.getLogger('RayHunterMonitor')

    def monitor_devices(self, poll_interval=30):
        """Continuous monitoring of multiple RayHunter devices"""
        while True:
            for device_name, config in self.devices.items():
                try:
                    device_status = self.check_device_status(config)
                    alerts = self.get_recent_alerts(config)

                    if alerts:
                        self.process_alerts(device_name, alerts)

                    self.log_device_status(device_name, device_status)

                except Exception as e:
                    self.logger.error(f"Error monitoring device {device_name}: {e}")

            time.sleep(poll_interval)

    def check_device_status(self, config):
        """Check comprehensive device status via API"""
        api_url = f"http://{config['ip']}:8080/api/status"

        try:
            response = requests.get(api_url, timeout=10)
            response.raise_for_status()

            status_data = response.json()
            return {
                'online': True,
                'battery_level': status_data.get('battery_level'),
                'signal_strength': status_data.get('signal_strength'),
                'recording_status': status_data.get('recording_active'),
                'last_alert': status_data.get('last_alert_time'),
                'heuristics_enabled': status_data.get('active_heuristics')
            }
        except requests.RequestException as e:
            self.logger.warning(f"Device {config['ip']} unreachable: {e}")
            return {'online': False, 'error': str(e)}

    def get_recent_alerts(self, config, minutes=5):
        """Retrieve recent alerts from device"""
        api_url = f"http://{config['ip']}:8080/api/alerts"
        params = {'since': f"{minutes}min"}

        try:
            response = requests.get(api_url, params=params, timeout=10)
            response.raise_for_status()
            return response.json().get('alerts', [])
        except requests.RequestException:
            return []

    def process_alerts(self, device_name, alerts):
        """Process and respond to alerts"""
        for alert in alerts:
            alert_level = self.assess_alert_severity(alert)

            if alert_level == 'CRITICAL':
                self.handle_critical_alert(device_name, alert)
            elif alert_level == 'HIGH':
                self.handle_high_alert(device_name, alert)
            elif alert_level == 'MEDIUM':
                self.handle_medium_alert(device_name, alert)

            # Log all alerts
            self.logger.info(f"Alert from {device_name}: {alert['heuristic']} - {alert_level}")

    def assess_alert_severity(self, alert):
        """Assess alert severity based on multiple factors"""
        threat_type = alert.get('heuristic', '')
        confidence = alert.get('confidence_score', 0)

        # Critical threats
        if threat_type in ['null_cipher_detection', 'imsi_request_detection'] and confidence > 0.9:
            return 'CRITICAL'

        # High severity threats
        elif threat_type in ['connection_release_detection', 'sib_downgrade_detection'] and confidence > 0.8:
            return 'HIGH'

        # Medium severity
        elif confidence > 0.6:
            return 'MEDIUM'

        return 'LOW'

    def handle_critical_alert(self, device_name, alert):
        """Handle critical security alerts with immediate response"""
        # Send immediate notifications
        self.send_sms_alert(f"CRITICAL: IMSI catcher detected by {device_name}")
        self.send_email_alert("CRITICAL THREAT", device_name, alert)

        # Execute automated response
        subprocess.run(['/opt/security/scripts/critical_response.sh', device_name])

        # Log to SIEM
        self.log_to_siem('CRITICAL', device_name, alert)
Integration in Unternehmenssysteme
SIEM-Integrationsskript:
def integrate_with_siem(self, alert_data):
    """Integration with enterprise SIEM systems"""

    # Splunk integration
    splunk_data = {
        'sourcetype': 'rayhunter:alert',
        'source': f"rayhunter:{alert_data['device_name']}",
        'time': int(time.time()),
        'event': {
            'threat_type': alert_data['heuristic'],
            'confidence': alert_data['confidence_score'],
            'device_location': alert_data.get('location'),
            'cellular_data': alert_data.get('cellular_parameters'),
            'severity': alert_data['severity']
        }
    }

    # Send to Splunk HEC
    requests.post(
        'https://splunk.company.com:8088/services/collector',
        headers={'Authorization': 'Splunk <HEC-TOKEN>'},
        json=splunk_data
    )

    # QRadar integration via syslog
    syslog_message = f"RayHunter ALERT: {alert_data['heuristic']} detected " \
                    f"with confidence {alert_data['confidence_score']:.2f} " \
                    f"on device {alert_data['device_name']}"

    subprocess.run([
        'logger', '-p', 'local0.alert', '-t', 'RayHunter', syslog_message
    ])
Mehrere Geräte koordinieren
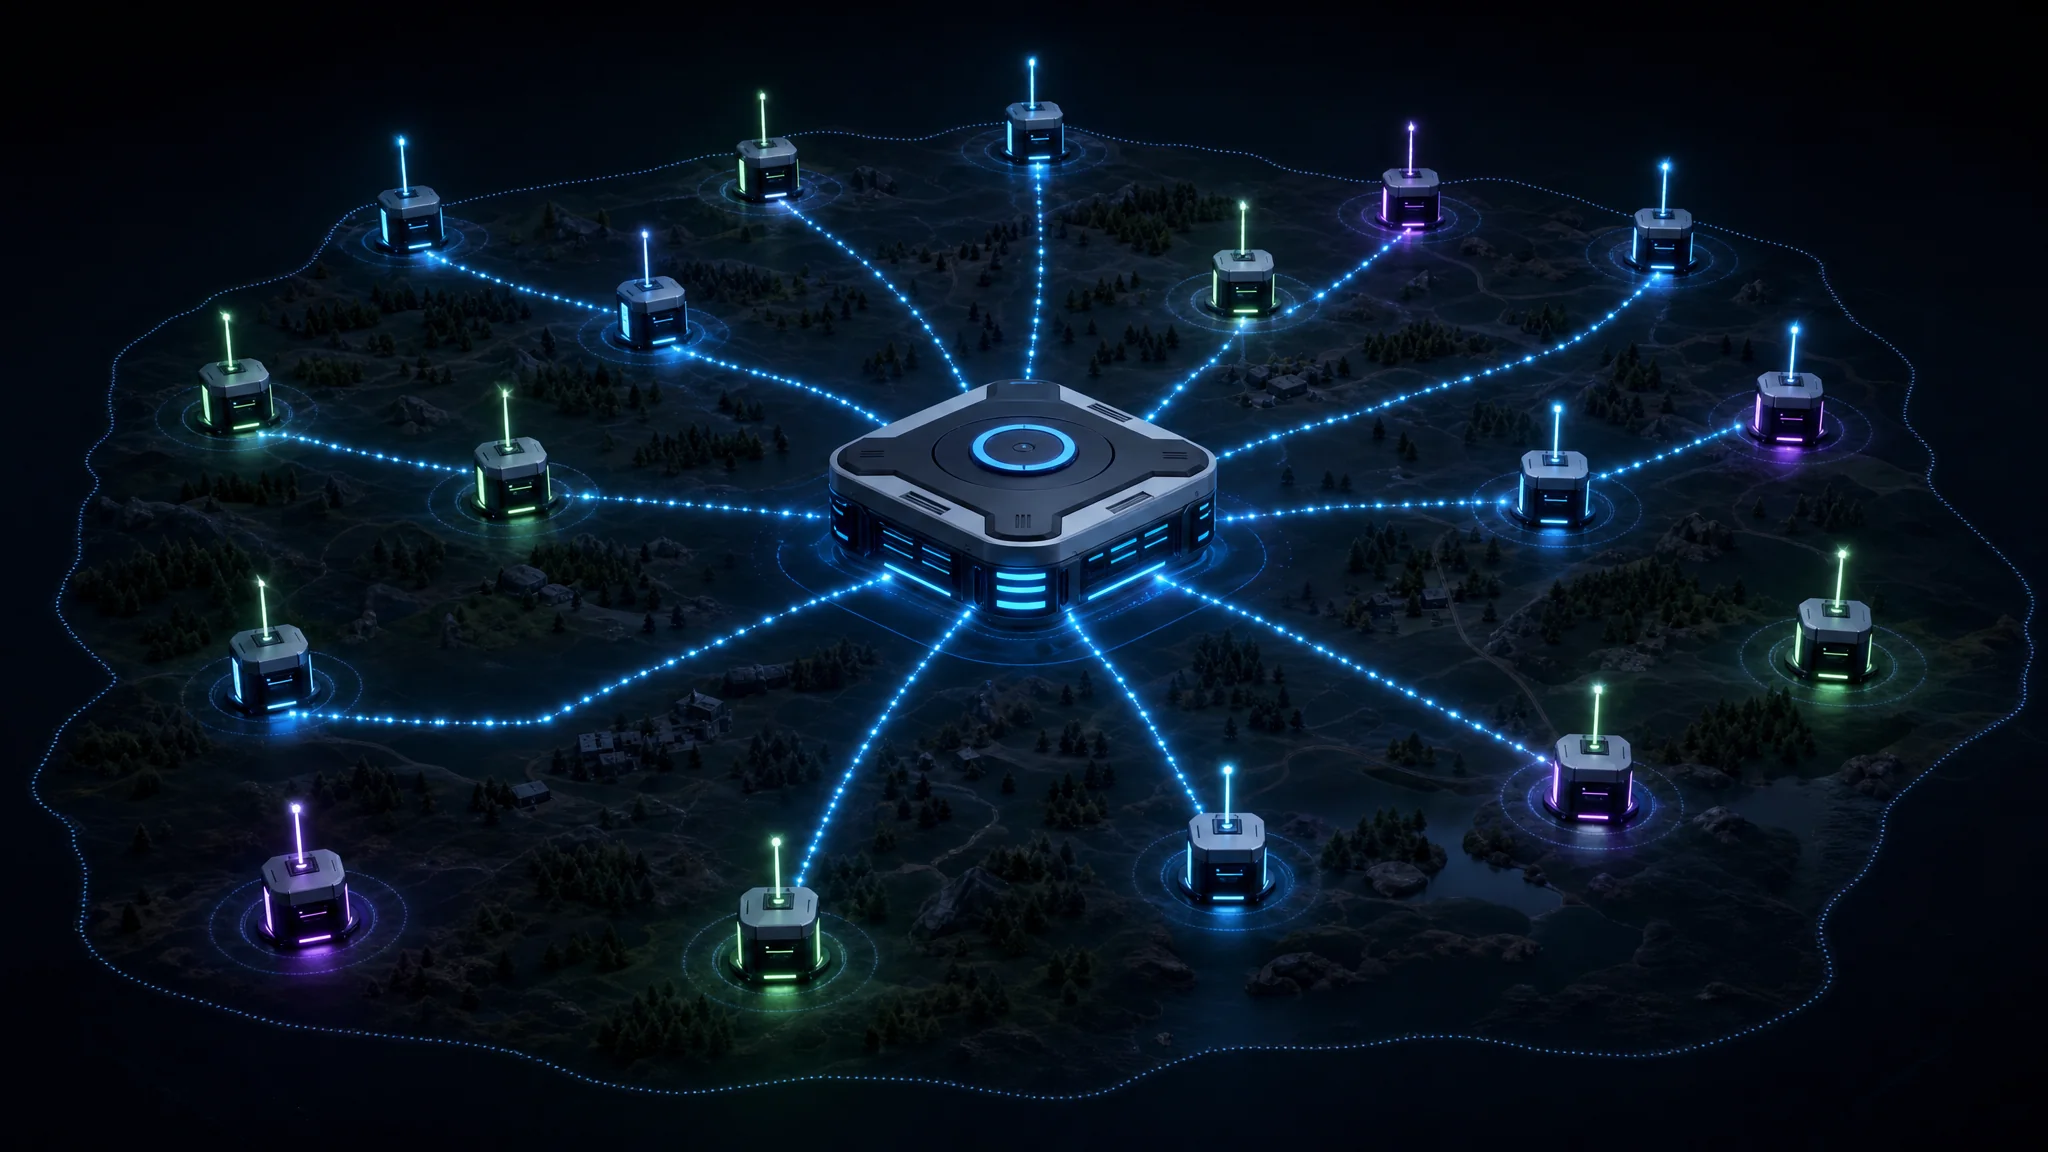
Bei fortgeschrittenen RayHunter-Einsätzen arbeiten oft mehrere Geräte zusammen, um ein Gebiet umfassend abzudecken und Bedrohungen gegenseitig zu bestätigen.
Koordinierte Erkennungsnetzwerke
Master-Slave-Konfiguration:
[coordination]
# Master device configuration
role = "master"
slave_devices = [
    { ip = "192.168.1.101", name = "rayhunter-north", priority = 1 },
    { ip = "192.168.1.102", name = "rayhunter-south", priority = 2 },
    { ip = "192.168.1.103", name = "rayhunter-west", priority = 3 }
]

# Coordination settings
sync_interval = 30              # Sync every 30 seconds
correlation_window = 60         # 1 minute correlation window
consensus_threshold = 0.67      # 67% agreement required for alert
automatic_failover = true
heartbeat_timeout = 120         # 2 minutes heartbeat timeout

# Alert distribution
distribute_alerts = true
alert_consolidation = true
duplicate_suppression = true
cross_validation_required = true
Konfiguration eines Slave-Geräts:
[coordination]
# Slave device configuration
role = "slave"
master_device = { ip = "192.168.1.100", name = "rayhunter-master" }

# Reporting settings
report_interval = 15            # Report every 15 seconds
include_negative_results = true # Report lack of threats too
local_decision_making = false   # Defer to master
emergency_autonomous_mode = true # Act independently if master unavailable
Skripte für koordinierte Analysen
Bedrohungen zwischen Geräten korrelieren:
#!/usr/bin/env python3
"""
Multi-Device RayHunter Coordination System
Provides coordinated threat detection across multiple devices
"""

import asyncio
import aiohttp
import json
from datetime import datetime, timedelta
import numpy as np

class CoordinatedDetectionSystem:
    def __init__(self, device_network):
        self.devices = device_network
        self.correlation_matrix = {}
        self.active_threats = {}

    async def coordinate_detection(self):
        """Main coordination loop"""
        while True:
            # Collect data from all devices
            device_data = await self.collect_device_data()

            # Perform correlation analysis
            correlated_threats = self.correlate_threats(device_data)

            # Validate threats through consensus
            validated_threats = self.consensus_validation(correlated_threats)

            # Distribute validated threats back to devices
            await self.distribute_threat_intelligence(validated_threats)

            await asyncio.sleep(30)  # 30-second coordination cycle

    async def collect_device_data(self):
        """Collect data from all devices in parallel"""
        tasks = []
        for device in self.devices:
            task = self.get_device_data(device)
            tasks.append(task)

        results = await asyncio.gather(*tasks, return_exceptions=True)
        return {device['name']: result for device, result in zip(self.devices, results)}

    async def get_device_data(self, device):
        """Get data from individual device"""
        async with aiohttp.ClientSession() as session:
            try:
                # Get recent alerts
                alerts_url = f"http://{device['ip']}:8080/api/alerts?since=1min"
                async with session.get(alerts_url) as response:
                    alerts_data = await response.json()

                # Get device status
                status_url = f"http://{device['ip']}:8080/api/status"
                async with session.get(status_url) as response:
                    status_data = await response.json()

                return {
                    'alerts': alerts_data.get('alerts', []),
                    'status': status_data,
                    'timestamp': datetime.now().isoformat()
                }
            except Exception as e:
                return {'error': str(e), 'timestamp': datetime.now().isoformat()}

    def correlate_threats(self, device_data):
        """Correlate threats across multiple devices"""
        correlated_threats = []

        # Extract all alerts from all devices
        all_alerts = []
        for device_name, data in device_data.items():
            if 'alerts' in data:
                for alert in data['alerts']:
                    alert['source_device'] = device_name
                    all_alerts.append(alert)

        # Group alerts by time and threat type
        threat_groups = self.group_alerts_by_similarity(all_alerts)

        for group in threat_groups:
            if len(group) >= 2:  # Multiple devices detected similar threats
                correlated_threat = self.create_correlated_threat(group)
                correlated_threats.append(correlated_threat)

        return correlated_threats

    def group_alerts_by_similarity(self, alerts, time_window=60):
        """Group alerts by temporal and threat similarity"""
        groups = []
        processed_alerts = set()

        for i, alert1 in enumerate(alerts):
            if i in processed_alerts:
                continue

            group = [alert1]
            processed_alerts.add(i)

            alert1_time = datetime.fromisoformat(alert1['timestamp'])

            for j, alert2 in enumerate(alerts[i+1:], i+1):
                if j in processed_alerts:
                    continue

                alert2_time = datetime.fromisoformat(alert2['timestamp'])
                time_diff = abs((alert1_time - alert2_time).total_seconds())

                if (time_diff <= time_window and
                    alert1['heuristic'] == alert2['heuristic'] and
                    alert1['source_device'] != alert2['source_device']):

                    group.append(alert2)
                    processed_alerts.add(j)

            groups.append(group)

        return groups

    def consensus_validation(self, correlated_threats):
        """Validate threats through device consensus"""
        validated_threats = []

        for threat in correlated_threats:
            device_count = len(set(alert['source_device'] for alert in threat['constituent_alerts']))
            confidence_scores = [alert['confidence_score'] for alert in threat['constituent_alerts']]

            # Require minimum number of devices and confidence threshold
            if (device_count >= 2 and
                np.mean(confidence_scores) >= 0.7 and
                min(confidence_scores) >= 0.5):

                threat['validated'] = True
                threat['consensus_strength'] = device_count / len(self.devices)
                threat['confidence_score'] = np.mean(confidence_scores)
                validated_threats.append(threat)

        return validated_threats
Fortgeschrittene Probleme beheben
Häufige fortgeschrittene Probleme
Probleme bei der Leistungsoptimierung
Hohe CPU-Auslastung beheben:
#!/bin/bash
# RayHunter performance troubleshooting script

echo "=== RayHunter Performance Analysis ==="

# Check CPU usage
echo "Current CPU usage:"
top -bn1 | grep rayhunter

# Check memory usage
echo -e "\nMemory usage:"
ps aux | grep rayhunter | awk '{print $4, $6, $11}'

# Check disk I/O
echo -e "\nDisk I/O:"
iotop -a -o -d1 -n3 | grep rayhunter

# Analyze configuration issues
echo -e "\nConfiguration analysis:"
if [ -f /data/rayhunter/config.toml ]; then
    # Check for resource-intensive configurations
    grep -E "test_heuristic.*true|sensitivity.*maximum|debug.*true" /data/rayhunter/config.toml

    # Check recording settings
    grep -E "recording|storage" /data/rayhunter/config.toml
else
    echo "Config file not found!"
fi

# Check for excessive logging
echo -e "\nLog file sizes:"
du -sh /data/rayhunter/logs/*

# Network performance check
echo -e "\nNetwork performance:"
netstat -i | grep -E "wlan|eth"

# Generate optimization recommendations
echo -e "\n=== Optimization Recommendations ==="

# Check if test heuristic is enabled
if grep -q "test_heuristic.*=.*true" /data/rayhunter/config.toml; then
    echo "⚠️  Test heuristic is enabled - disable for production use"
fi

# Check sensitivity settings
if grep -q "sensitivity.*=.*\"maximum\"" /data/rayhunter/config.toml; then
    echo "⚠️  Maximum sensitivity may cause high CPU usage in dense environments"
fi

# Check storage settings
STORAGE_USED=$(df -h /data/rayhunter | awk 'NR==2 {print $5}' | sed 's/%//')
if [ "$STORAGE_USED" -gt 80 ]; then
    echo "⚠️  Storage usage is ${STORAGE_USED}% - clean up old recordings"
fi
Speicherlecks erkennen und beheben:
#!/bin/bash
# Memory leak detection and automatic remediation

MEMORY_THRESHOLD=80  # 80% memory usage threshold
LOG_FILE="/var/log/rayhunter/memory_monitor.log"

monitor_memory() {
    while true; do
        # Get RayHunter memory usage
        MEMORY_USAGE=$(ps aux | grep rayhunter-daemon | grep -v grep | awk '{print $4}')

        if [ ! -z "$MEMORY_USAGE" ]; then
            MEMORY_PERCENT=$(echo "$MEMORY_USAGE" | cut -d. -f1)

            echo "$(date): RayHunter memory usage: ${MEMORY_USAGE}%" >> "$LOG_FILE"

            if [ "$MEMORY_PERCENT" -gt "$MEMORY_THRESHOLD" ]; then
                echo "$(date): High memory usage detected: ${MEMORY_USAGE}%" >> "$LOG_FILE"

                # Attempt graceful restart
                echo "$(date): Attempting graceful restart..." >> "$LOG_FILE"
                systemctl restart rayhunter_daemon

                sleep 30

                # Verify restart was successful
                if pgrep rayhunter-daemon > /dev/null; then
                    echo "$(date): Graceful restart successful" >> "$LOG_FILE"
                else
                    echo "$(date): Graceful restart failed, attempting force restart" >> "$LOG_FILE"
                    killall -9 rayhunter-daemon
                    systemctl start rayhunter_daemon
                fi
            fi
        fi

        sleep 60  # Check every minute
    done
}

# Run memory monitoring in background
monitor_memory &
Probleme mit der Netzwerkverbindung
Fortgeschrittene Verbindungsdiagnose:
#!/bin/bash
# Advanced RayHunter connectivity troubleshooting

echo "=== RayHunter Network Diagnostics ==="

# Check basic connectivity
echo "1. Basic connectivity check:"
ping -c 3 8.8.8.8 > /dev/null 2>&1
if [ $? -eq 0 ]; then
    echo "✓ Internet connectivity: OK"
else
    echo "✗ Internet connectivity: FAILED"
fi

# Check cellular connection
echo -e "\n2. Cellular connection analysis:"
if command -v qmicli &> /dev/null; then
    # Check modem status
    qmicli -d /dev/cdc-wdm0 --dms-get-operating-mode
    qmicli -d /dev/cdc-wdm0 --nas-get-signal-strength
    qmicli -d /dev/cdc-wdm0 --nas-get-serving-system
else
    echo "qmicli not available - using alternative methods"

    # Check network interfaces
    ip addr show | grep -A 10 wwan

    # Check routing
    ip route show
fi

# Check RayHunter web interface
echo -e "\n3. RayHunter web interface check:"
for port in 8080 80; do
    if netstat -tuln | grep ":$port " > /dev/null; then
        echo "✓ Port $port is listening"

        # Test HTTP response
        if curl -s -o /dev/null -w "%{http_code}" "http://localhost:$port" | grep -q "200\|302"; then
            echo "✓ HTTP service responding on port $port"
        else
            echo "✗ HTTP service not responding properly on port $port"
        fi
    else
        echo "✗ Port $port is not listening"
    fi
done

# Check cellular diagnostics interface
echo -e "\n4. Cellular diagnostics interface:"
if [ -c /dev/diag ]; then
    echo "✓ /dev/diag interface available"
    ls -la /dev/diag
else
    echo "✗ /dev/diag interface not available"
    echo "Checking alternative interfaces:"
    ls -la /dev/ | grep -E "ttyUSB|cdc-wdm|qcserial"
fi

# Advanced network analysis
echo -e "\n5. Advanced network analysis:"

# Check APN settings
echo "Current APN configuration:"
grep -r "apn" /etc/NetworkManager/system-connections/ 2>/dev/null || echo "No APN config found"

# Check DNS resolution
echo "DNS resolution test:"
nslookup google.com | head -5

# Check firewall rules
echo "Firewall rules affecting RayHunter:"
iptables -L | grep -E "8080|rayhunter" || echo "No specific firewall rules found"
Gerätespezifische Fehlerbehebung
Fortgeschrittene Fehlerbehebung beim Orbic RC400L:
#!/bin/bash
# Orbic RC400L specific troubleshooting procedures

echo "=== Orbic RC400L Advanced Diagnostics ==="

# Check bootloader and system partition status
echo "1. System partition analysis:"
df -h | grep -E "/system|/data|/usrdata"

# Check Android subsystem
echo -e "\n2. Android subsystem check:"
if command -v adb &> /dev/null; then
    adb devices
    if adb devices | grep -q "device$"; then
        echo "✓ ADB connection available"

        # Check system properties
        adb shell getprop | grep -E "ro.build|persist.vendor"

        # Check running processes
        adb shell ps | grep rayhunter

        # Check system logs
        echo "Recent system errors:"
        adb logcat -d | grep -E "ERROR|FATAL" | tail -10
    else
        echo "✗ No ADB connection available"
    fi
else
    echo "ADB not available - using alternative methods"
fi

# Check modem firmware
echo -e "\n3. Modem firmware analysis:"
if [ -c /dev/diag ]; then
    # Use custom tool to query modem firmware
    python3 << 'EOF'
import serial
import struct
import time

try:
    # Open diagnostic interface
    diag = serial.Serial('/dev/diag', 115200, timeout=1)

    # Query firmware version (simplified)
    # This would require proper DIAG protocol implementation
    print("Modem diagnostic interface accessible")
    diag.close()
except Exception as e:
    print(f"Modem diagnostic access failed: {e}")
EOF
fi

# Check carrier-specific issues
echo -e "\n4. Carrier configuration check:"
echo "Current band preferences:"
cat /data/rayhunter/config.toml | grep -A 5 -B 5 "band"

echo "Network registration status:"
# Check registration with all available carriers
if command -v qmicli &> /dev/null; then
    qmicli -d /dev/cdc-wdm0 --nas-get-home-network
    qmicli -d /dev/cdc-wdm0 --nas-get-preferred-networks
fi
Fehlerbehebung beim TP-Link M7350:
#!/bin/bash
# TP-Link M7350 specific troubleshooting

echo "=== TP-Link M7350 Advanced Diagnostics ==="

# Check SD card functionality
echo "1. SD card diagnostics:"
if mountpoint -q /media/sd; then
    echo "✓ SD card is mounted"
    df -h /media/sd

    # Check SD card health
    echo "SD card filesystem check:"
    fsck -n /dev/mmcblk0p1 2>&1 | head -10

    # Check write permissions
    touch /media/sd/test_write 2>/dev/null && rm /media/sd/test_write
    if [ $? -eq 0 ]; then
        echo "✓ SD card write permissions OK"
    else
        echo "✗ SD card write permissions failed"
    fi
else
    echo "✗ SD card not mounted"
    echo "Available block devices:"
    lsblk | grep -E "mmc|sd"
fi

# Check OpenWrt system
echo -e "\n2. OpenWrt system analysis:"
echo "System information:"
cat /proc/version
uname -a

echo "Available memory:"
free -h

echo "System load:"
uptime

# Check package installation
echo "Installed packages relevant to RayHunter:"
opkg list-installed | grep -E "python|kmod|usb"

# Check kernel modules
echo -e "\n3. Kernel module status:"
lsmod | grep -E "diag|qmi|cdc|usb"

# Check USB diagnostic interface
echo "USB diagnostic devices:"
lsusb -t
ls -la /dev/ttyUSB* 2>/dev/null || echo "No USB serial devices found"
Wiederherstellungsverfahren
Skripte zur Systemwiederherstellung:
#!/bin/bash
# Emergency RayHunter system recovery

BACKUP_DIR="/data/rayhunter/backup"
CONFIG_FILE="/data/rayhunter/config.toml"
RECOVERY_LOG="/var/log/rayhunter/recovery.log"

log_message() {
    echo "$(date): $1" | tee -a "$RECOVERY_LOG"
}

create_backup() {
    log_message "Creating system backup..."
    mkdir -p "$BACKUP_DIR"

    # Backup configuration
    cp "$CONFIG_FILE" "$BACKUP_DIR/config_$(date +%Y%m%d_%H%M%S).toml"

    # Backup recordings (last 24 hours)
    find /data/rayhunter/recordings -name "*.qmdl" -mtime -1 -exec cp {} "$BACKUP_DIR/" \;

    # Backup logs
    tar -czf "$BACKUP_DIR/logs_$(date +%Y%m%d_%H%M%S).tar.gz" /data/rayhunter/logs/

    log_message "Backup completed"
}

reset_configuration() {
    log_message "Resetting configuration to defaults..."

    # Stop RayHunter service
    systemctl stop rayhunter_daemon

    # Reset to factory configuration
    cp /etc/rayhunter/config.toml.default "$CONFIG_FILE"

    # Clear problematic cache files
    rm -f /data/rayhunter/cache/*

    # Reset permissions
    chown -R rayhunter:rayhunter /data/rayhunter/
    chmod -R 755 /data/rayhunter/

    log_message "Configuration reset completed"
}

factory_reset() {
    log_message "Performing factory reset..."

    # Create backup first
    create_backup

    # Stop all RayHunter services
    systemctl stop rayhunter_daemon
    systemctl disable rayhunter_daemon

    # Remove all RayHunter data (except backups)
    find /data/rayhunter -type f ! -path "*/backup/*" -delete

    # Reinstall RayHunter
    cd /tmp
    wget -O rayhunter-latest.zip "https://github.com/EFForg/rayhunter/releases/latest/download/rayhunter-linux-x64.zip"
    unzip rayhunter-latest.zip
    ./installer $(detect_device_type)

    log_message "Factory reset completed"
}

detect_device_type() {
    # Auto-detect device type for reinstallation
    if grep -q "Orbic" /proc/cpuinfo || [ -d "/android_root" ]; then
        echo "orbic"
    elif grep -q "MT7620" /proc/cpuinfo || [ -f "/etc/openwrt_version" ]; then
        echo "tplink"
    else
        echo "unknown"
    fi
}

# Main recovery menu
echo "=== RayHunter Emergency Recovery ==="
echo "1. Create backup only"
echo "2. Reset configuration to defaults"
echo "3. Factory reset (destructive)"
echo "4. System diagnostics"
echo "5. Exit"

read -p "Select option (1-5): " choice

case $choice in
    1) create_backup ;;
    2) reset_configuration ;;
    3)
        read -p "Are you sure? This will erase all data except backups (y/N): " confirm
        if [ "$confirm" = "y" ] || [ "$confirm" = "Y" ]; then
            factory_reset
        else
            echo "Factory reset cancelled"
        fi
        ;;
    4)
        echo "Running system diagnostics..."
        # Run all diagnostic scripts
        /opt/rayhunter/scripts/performance_check.sh
        /opt/rayhunter/scripts/network_diagnostics.sh
        ;;
    5) exit 0 ;;
    *) echo "Invalid option" ;;
esac
Integrationsszenarien für Experten
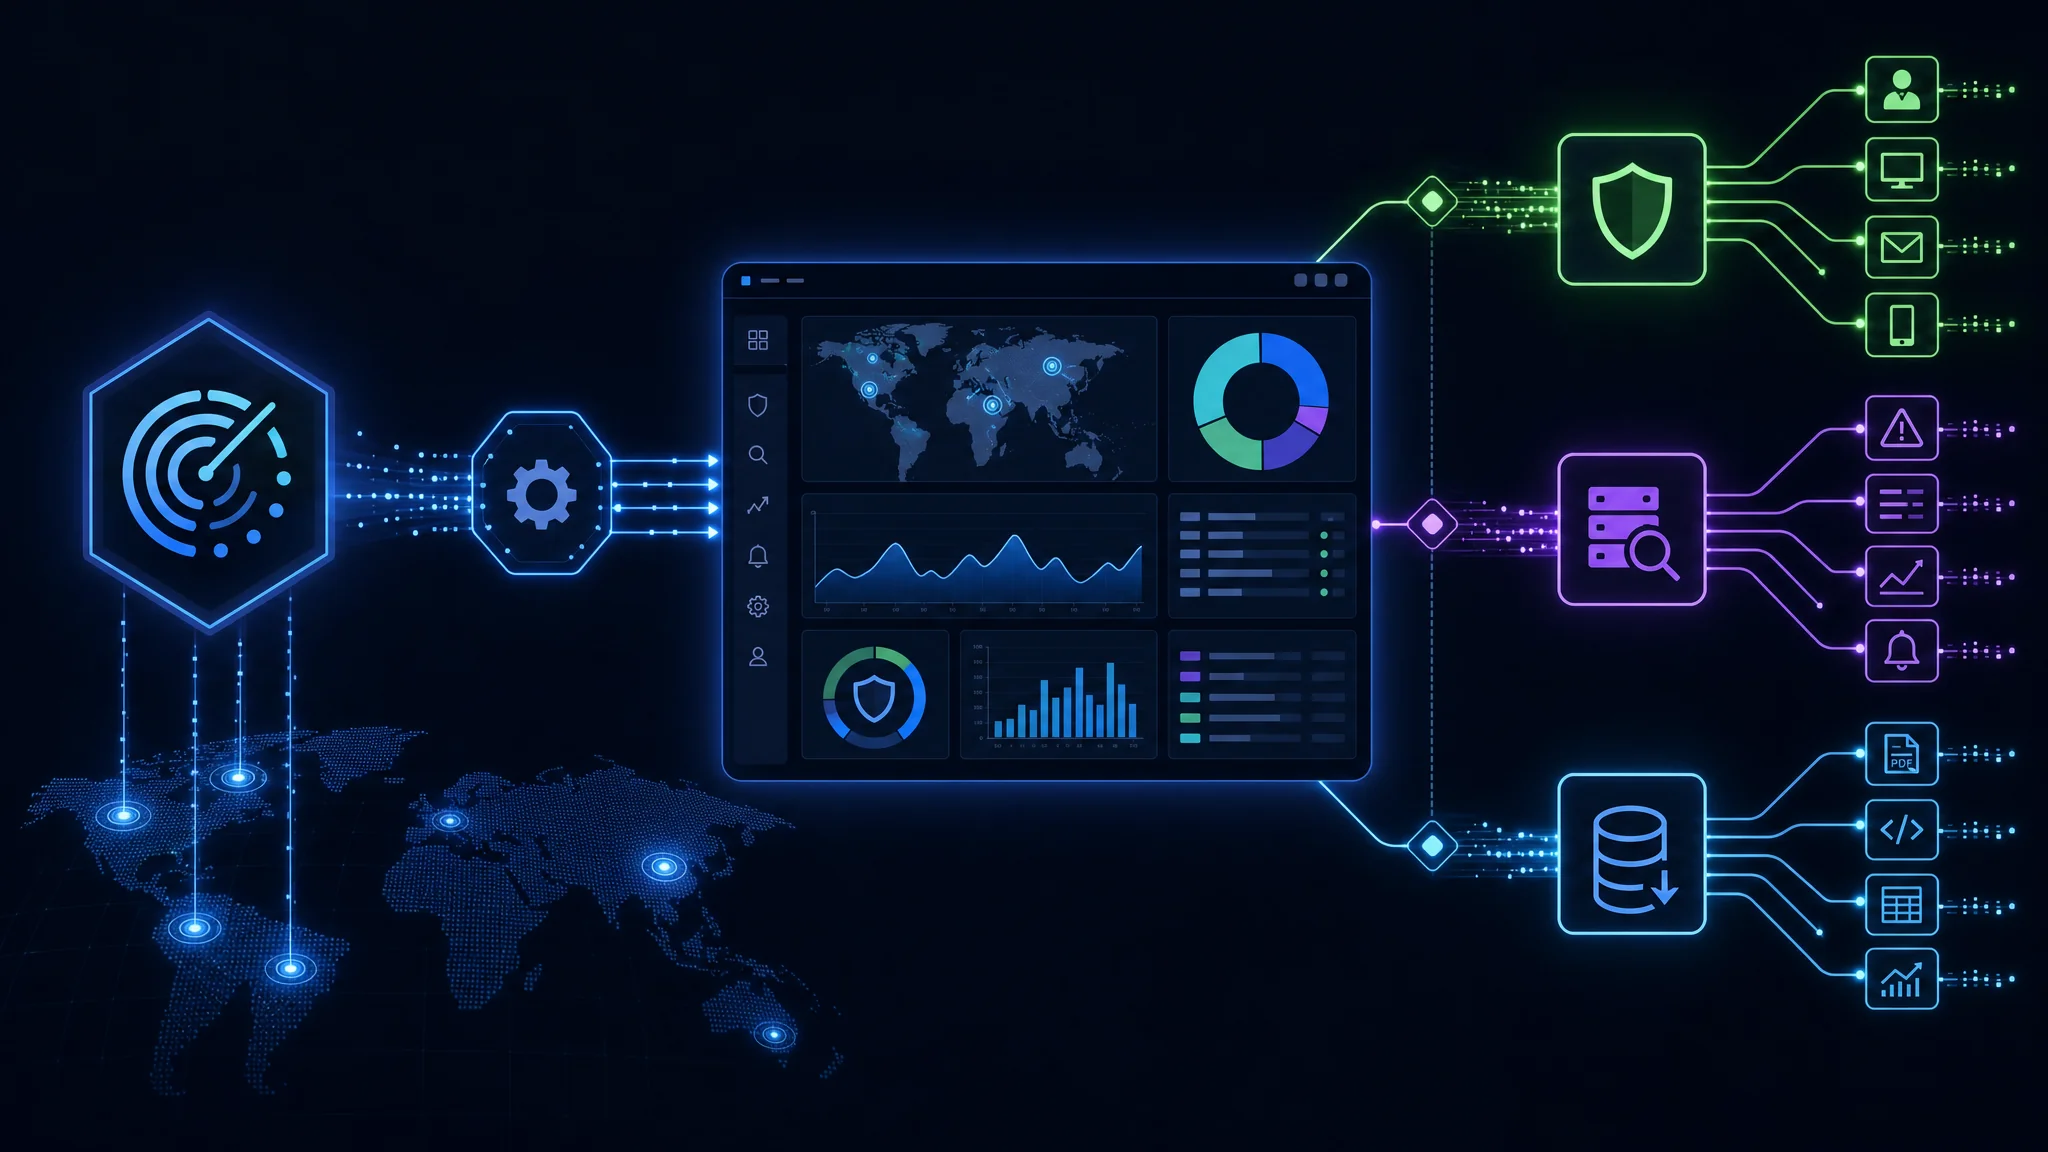
Integration in Forschungsumgebungen
Konfiguration für akademische Forschung:
#!/usr/bin/env python3
"""
RayHunter Research Integration Platform
Advanced configuration for academic cellular security research
"""

import pandas as pd
import numpy as np
import matplotlib.pyplot as plt
import seaborn as sns
from scipy import signal, stats
import json
import sqlite3
from datetime import datetime, timedelta

class RayHunterResearchPlatform:
    def __init__(self, research_db="/data/research/rayhunter_research.db"):
        self.db_path = research_db
        self.setup_research_database()

    def setup_research_database(self):
        """Setup comprehensive research database schema"""
        conn = sqlite3.connect(self.db_path)
        cursor = conn.cursor()

        # Extended schema for research data
        cursor.execute('''
            CREATE TABLE IF NOT EXISTS research_sessions (
                session_id TEXT PRIMARY KEY,
                start_time TEXT,
                end_time TEXT,
                location TEXT,
                environment_type TEXT,
                device_configuration TEXT,
                research_objectives TEXT,
                metadata JSON
            )
        ''')

        cursor.execute('''
            CREATE TABLE IF NOT EXISTS cellular_measurements (
                id INTEGER PRIMARY KEY,
                session_id TEXT,
                timestamp TEXT,
                cell_id INTEGER,
                lac INTEGER,
                mcc INTEGER,
                mnc INTEGER,
                signal_strength INTEGER,
                signal_quality INTEGER,
                frequency_band TEXT,
                technology TEXT,
                serving_cell BOOLEAN,
                FOREIGN KEY (session_id) REFERENCES research_sessions (session_id)
            )
        ''')

        cursor.execute('''
            CREATE TABLE IF NOT EXISTS threat_observations (
                id INTEGER PRIMARY KEY,
                session_id TEXT,
                timestamp TEXT,
                threat_type TEXT,
                heuristic_triggered TEXT,
                confidence_score REAL,
                false_positive_assessment TEXT,
                validation_method TEXT,
                researcher_notes TEXT,
                FOREIGN KEY (session_id) REFERENCES research_sessions (session_id)
            )
        ''')

        conn.commit()
        conn.close()

    def conduct_controlled_experiment(self, experiment_config):
        """Conduct controlled experiment with specified parameters"""
        session_id = f"exp_{datetime.now().strftime('%Y%m%d_%H%M%S')}"

        # Configure RayHunter for experiment
        self.configure_rayhunter_for_research(experiment_config)

        # Start data collection
        collection_start = datetime.now()

        # Run experiment for specified duration
        experiment_duration = experiment_config.get('duration_minutes', 60)

        # Collect baseline measurements
        baseline_data = self.collect_baseline_measurements(experiment_duration // 3)

        # Introduce controlled variables if specified
        if experiment_config.get('introduce_threats', False):
            threat_data = self.simulate_threat_scenarios(experiment_config['threat_scenarios'])

        # Collect post-intervention data
        post_data = self.collect_post_measurements(experiment_duration // 3)

        # Analyze results
        analysis_results = self.analyze_experiment_results(
            session_id, baseline_data, post_data
        )

        return {
            'session_id': session_id,
            'duration': experiment_duration,
            'analysis': analysis_results,
            'raw_data_location': f"/data/research/sessions/{session_id}"
        }

    def statistical_threat_analysis(self, time_period_days=30):
        """Perform statistical analysis of threat detection patterns"""
        conn = sqlite3.connect(self.db_path)

        # Query threat observations
        end_date = datetime.now()
        start_date = end_date - timedelta(days=time_period_days)

        query = """
            SELECT t.*, s.environment_type, s.location
            FROM threat_observations t
            JOIN research_sessions s ON t.session_id = s.session_id
            WHERE t.timestamp BETWEEN ? AND ?
        """

        df = pd.read_sql_query(query, conn, params=(start_date.isoformat(), end_date.isoformat()))
        conn.close()

        if df.empty:
            return {"error": "No data available for analysis"}

        # Statistical analysis
        analysis = {
            'descriptive_stats': {
                'total_observations': len(df),
                'unique_threat_types': df['threat_type'].nunique(),
                'mean_confidence': df['confidence_score'].mean(),
                'std_confidence': df['confidence_score'].std()
            },
            'threat_distribution': df['threat_type'].value_counts().to_dict(),
            'environmental_correlation': {},
            'temporal_patterns': self.analyze_temporal_patterns(df),
            'false_positive_analysis': self.analyze_false_positives(df)
        }

        # Environment correlation analysis
        for env_type in df['environment_type'].unique():
            env_data = df[df['environment_type'] == env_type]
            analysis['environmental_correlation'][env_type] = {
                'threat_frequency': len(env_data) / time_period_days,
                'average_confidence': env_data['confidence_score'].mean(),
                'threat_type_distribution': env_data['threat_type'].value_counts().to_dict()
            }

        # Generate visualizations
        self.generate_research_visualizations(df, analysis)

        return analysis

    def generate_research_visualizations(self, df, analysis):
        """Generate comprehensive research visualizations"""
        fig, axes = plt.subplots(2, 3, figsize=(20, 12))

        # Threat type distribution
        threat_counts = df['threat_type'].value_counts()
        axes[0, 0].pie(threat_counts.values, labels=threat_counts.index, autopct='%1.1f%%')
        axes[0, 0].set_title('Threat Type Distribution')

        # Confidence score distribution
        axes[0, 1].hist(df['confidence_score'], bins=20, alpha=0.7)
        axes[0, 1].set_title('Confidence Score Distribution')
        axes[0, 1].set_xlabel('Confidence Score')
        axes[0, 1].set_ylabel('Frequency')

        # Temporal patterns
        df['hour'] = pd.to_datetime(df['timestamp']).dt.hour
        hourly_counts = df.groupby('hour').size()
        axes[0, 2].bar(hourly_counts.index, hourly_counts.values)
        axes[0, 2].set_title('Threats by Hour of Day')
        axes[0, 2].set_xlabel('Hour')
        axes[0, 2].set_ylabel('Threat Count')

        # Environment vs confidence
        sns.boxplot(data=df, x='environment_type', y='confidence_score', ax=axes[1, 0])
        axes[1, 0].set_title('Confidence by Environment Type')
        axes[1, 0].tick_params(axis='x', rotation=45)

        # Correlation heatmap
        numeric_df = df.select_dtypes(include=[np.number])
        correlation_matrix = numeric_df.corr()
        sns.heatmap(correlation_matrix, annot=True, ax=axes[1, 1])
        axes[1, 1].set_title('Correlation Matrix')

        # False positive analysis
        if 'false_positive_assessment' in df.columns:
            fp_data = df['false_positive_assessment'].value_counts()
            axes[1, 2].bar(fp_data.index, fp_data.values)
            axes[1, 2].set_title('False Positive Assessment')
            axes[1, 2].tick_params(axis='x', rotation=45)

        plt.tight_layout()
        plt.savefig(f'/data/research/analysis/visualization_{datetime.now().strftime("%Y%m%d_%H%M%S")}.png',
                   dpi=300, bbox_inches='tight')
        plt.close()

    def export_research_data(self, format='csv', time_range_days=None):
        """Export research data in various formats for external analysis"""
        conn = sqlite3.connect(self.db_path)

        if time_range_days:
            end_date = datetime.now()
            start_date = end_date - timedelta(days=time_range_days)
            date_filter = f"WHERE timestamp BETWEEN '{start_date.isoformat()}' AND '{end_date.isoformat()}'"
        else:
            date_filter = ""

        # Export threat observations
        threat_query = f"SELECT * FROM threat_observations {date_filter}"
        threat_df = pd.read_sql_query(threat_query, conn)

        # Export cellular measurements
        cellular_query = f"SELECT * FROM cellular_measurements {date_filter}"
        cellular_df = pd.read_sql_query(cellular_query, conn)

        conn.close()

        timestamp = datetime.now().strftime("%Y%m%d_%H%M%S")

        if format.lower() == 'csv':
            threat_df.to_csv(f'/data/research/exports/threats_{timestamp}.csv', index=False)
            cellular_df.to_csv(f'/data/research/exports/cellular_{timestamp}.csv', index=False)
        elif format.lower() == 'json':
            threat_df.to_json(f'/data/research/exports/threats_{timestamp}.json', orient='records')
            cellular_df.to_json(f'/data/research/exports/cellular_{timestamp}.json', orient='records')
        elif format.lower() == 'parquet':
            threat_df.to_parquet(f'/data/research/exports/threats_{timestamp}.parquet')
            cellular_df.to_parquet(f'/data/research/exports/cellular_{timestamp}.parquet')

        return {
            'export_format': format,
            'threats_records': len(threat_df),
            'cellular_records': len(cellular_df),
            'export_timestamp': timestamp
        }
Fazit
Der fortgeschrittene Einsatz von RayHunter erfordert technisches Fachwissen in mehreren Bereichen, darunter Mobilfunkprotokolle, HF-Analyse, Systemintegration und Bedrohungsmodellierung. Die in diesem Leitfaden beschriebenen Techniken helfen Experten, die Erkennungsfunktionen von RayHunter optimal zu nutzen und zugleich Fehlalarme und Betriebsaufwand zu verringern.
Das sind die wichtigsten Punkte zum fortgeschrittenen RayHunter-Betrieb:
- Optimierte eigene Heuristiken können Fehlalarme um 80 % senken und die hohe Erkennungsempfindlichkeit erhalten, wenn sie an die Umgebung angepasst sind
- Automatisierung über APIs ermöglicht den Einsatz im Unternehmensmaßstab und die Integration in bestehende Security Operations Center
- Koordinierte Geräte decken Gebiete umfassend ab und gleichen Erkennungen gegenseitig ab, damit Bedrohungen zuverlässiger erkannt werden
- Fortgeschrittene Fehlersuche sorgt für zuverlässigen Betrieb in unterschiedlichen und anspruchsvollen Umgebungen
- Forschungsintegration unterstützt akademische und kommerzielle Forschung zu Bedrohungen in Mobilfunknetzen
Erfahrene RayHunter-Nutzer sollten Entwicklungen bei Mobilfunksicherheit, Überwachungstechnologie und quelloffenen Erkennungsfunktionen verfolgen. Sich verändernde Bedrohungen erfordern, Erkennungstechniken und Betriebsabläufe laufend zu verbessern.
Organisationen, die RayHunter professionell einsetzen, sollten die Integration in ein eigenes Security Operations Center, regelmäßige Schulungen für das Betriebspersonal und die Zusammenarbeit mit der RayHunter-Community einplanen, um Erkenntnisse zu Bedrohungen und Verbesserungen der Erkennung auszutauschen.
Du hast die Hardware für diese erweiterten Konfigurationen noch nicht? Geprüfte, mit RayHunter kompatible Geräte gibt es bei STS Collective. Mit dem Lesercode SIMEONONSECURITY erhältst du bis zu 20 % Rabatt.
Quellen
- Offizielle RayHunter-Dokumentation
- Referenz zur RayHunter REST API
- Electronic Frontier Foundation
- RayHunter-Repository auf GitHub
- Ressourcen zur Analyse von Mobilfunkprotokollen
- Ressourcen zu HF-Analyse und SDR
- Best Practices für die Integration von Unternehmenssicherheit

Disclosure and Affiliate Statement:
Partnerkennzeichnung: Wir können eine Provision durch Links auf dieser Seite verdienen. Diese Provisionen unterstützen unsere Website und den von uns bereitgestellten Inhalt. Seien Sie versichert, dass wir nur Produkte/Dienstleistungen empfehlen, von denen wir überzeugt sind. Vielen Dank für Ihr Vertrauen! Hier klicken, um mehr zu erfahren
Related Posts